News Intelligence
News Coverage, Breach Monitoring, And Analysis.
Two focused series: one tracks current news developments, the other connects freelance reporting on breaches and threats.
Cipher & Echo
Freelance
netPulz, Inc. curates this news and analysis library. Use breach reporting to identify questions for a review of business security controls. The Learning Center explains cybersecurity fundamentals; backup and disaster recovery planning addresses how operations can resume after disruption.
News Video Library
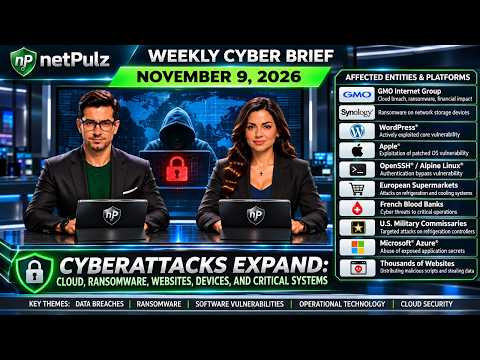
Join Cipher & Echo for the November 9, 2026, netPulz Weekly Cyber Brief as cyberattacks threaten businesses and critical infrastructure worldwide. This episode covers GMO Internet Group's cloud breach, Synology ransomware threats, WordPress vulnerabilities, Apple security flaws, and OpenSSH authentication risks affecting Alpine Linux. Discover emerging threats targeting European supermarkets, French blood banks, U.S. military commissaries, and Microsoft Azure cloud environments. We also examine malicious scripts compromising thousands of websites, exposing sensitive information and disrupting operations. Learn why timely patching, secure cloud identities, network segmentation, reliable backups, and continuous cybersecurity governance are essential to protecting organizations against evolving cyber threats.
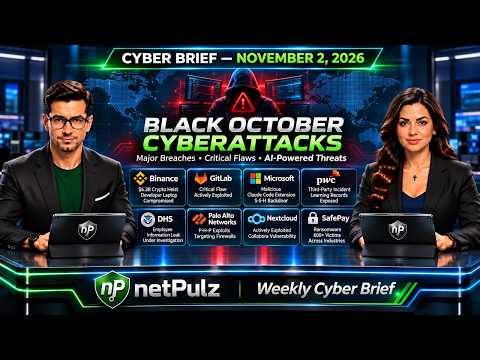
October’s alarming cybersecurity threats. This episode covers reported incidents involving Binance, GitLab, Microsoft, PwC, the Department of Homeland Security (DHS), Palo Alto Networks, Nextcloud, and SafePay ransomware. Discover how critical vulnerabilities, compromised developer tools, third-party breaches, stolen credentials, and AI-powered attacks threaten businesses and government agencies worldwide. Cipher & Echo explain emerging cyber risks, ransomware tactics, and practical defenses, including stronger authentication, timely patching, network segmentation, and secure backups. Stay informed about evolving threats and learn how organizations can strengthen cybersecurity resilience.
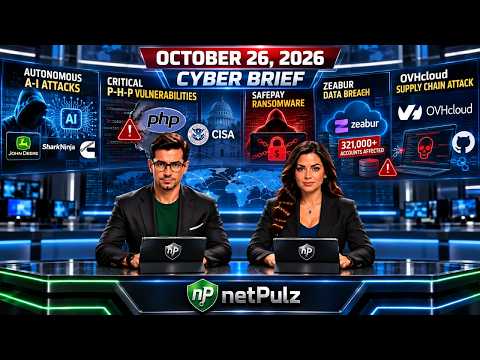
In this October 26, 2026 episode of Cipher & Echo Cyber Brief, we examine escalating cybersecurity threats, including autonomous AI-powered attacks targeting organizations such as John Deere, SharkNinja, and Cummins. We explore critical PHP vulnerabilities highlighted by CISA, the growing SafePay ransomware threat, and the Zeabur data breach reportedly affecting over 321,000 accounts. We also investigate the OVHcloud software supply chain compromise involving GitHub. Cipher and Echo explain how attackers exploit security weaknesses, compromised credentials, and vulnerable infrastructure. Discover why continuous cybersecurity governance, proactive vulnerability management, multifactor authentication, and tested recovery strategies are essential for protecting modern businesses against evolving cyber threats.
The Pentagon's Defense Manpower Data Center (DMDC) reportedly exposed over 3 million military and civilian personnel records in a major cybersecurity incident. In this Atlas & Zero episode, we examine how vulnerabilities in file-sharing systems, unencrypted sensitive information, and questions surrounding access controls and monitoring exposed critical security risks. Discover why Department of Defense (DoD) cybersecurity standards, NIST frameworks, and compliance requirements cannot guarantee protection without continuous enforcement. Atlas and Zero explore Zero Trust, encryption, vulnerability management, threat detection, and accountability while demonstrating why continuous cybersecurity governance is essential for protecting sensitive information and preventing devastating security failures across government and enterprise environments.
In this October 19, 2026 Weekly Cyber Brief, Cipher and Echo examine cyberattacks disrupting supermarket operations, critical security vulnerabilities, and emerging AI threats. Featured retailers include Carrefour, Intermarché, Netto, Cooperative U, Monoprix, and Ahold Delhaize. The episode explores security concerns involving Palo Alto Networks, Cisco, Ahsay, Ivanti, Citrix, Fortinet, and BeyondTrust. Cipher and Echo also discuss AI-powered attacks, exposed credentials, excessive permissions, and ransomware threats associated with Qilin and The Gentlemen. Discover why continuous cybersecurity governance, vulnerability management, secure remote access, and tested recovery strategies are essential for protecting businesses against increasingly sophisticated cyber threats worldwide.
In the October 12, 2026 Cyber Brief, Cipher & Echo examine escalating cyber threats affecting organizations worldwide. Discover reported breaches involving ASOS, Holland & Knight, and Squire Patton Boggs, alongside critical Citrix NetScaler vulnerabilities and Fortinet credential harvesting campaigns. Explore rising cyberattacks across South Korea and Japan, AI-assisted threats, and the FBI investigation involving ransomware recovery provider MonsterCloud. Learn how social engineering, stolen credentials, and unpatched systems expose businesses to serious risks. Cipher & Echo highlight essential cybersecurity defenses, including multi-factor authentication, continuous monitoring, incident response, and cybersecurity governance to help organizations strengthen resilience against evolving digital threats.
In the October 5, 2026 Cyber Brief, Cipher & Echo examine escalating AI-driven cyberattacks, ransomware, critical vulnerabilities, and major data breaches. Featured entities include Microsoft, Fortinet, Cisco, GitLab, Dell, Apple, Oracle PeopleSoft, Frontline Education, Technical University of Denmark, and the U.S. Department of Defense. The episode explores Warlock and KillSec ransomware operations, ShinyHunters threats, JadePuffer cloud attacks, and autonomous AI agents targeting government systems. Discover how attackers exploit enterprise infrastructure, compromise identities, and threaten critical services. Cipher & Echo highlight essential defenses, including vulnerability management, identity protection, vendor oversight, and continuous cybersecurity governance to strengthen organizational resilience.
Cipher and Echo examine the cybersecurity developments shaping this week’s threat landscape, including the Gyazo data breach disclosed by Helpfeel, active exploitation of Cisco Identity Services Engine, Oracle’s security updates, and CrowdSec’s findings from the TanStack supply chain attack. The episode also covers ISC BIND vulnerabilities threatening DNS availability and intrusions affecting two Colorado water utilities. Discover why exposed credentials, vulnerable infrastructure, and software dependencies demand coordinated attention. With clear distinctions between confirmed findings and ongoing investigations, this September 28, 2026 Weekly Cyber Brief highlights practical lessons in patching, access control, incident response, and continuous cybersecurity governance. Stay informed with netPulz.
Atlas & Zero examine the developing FBI breach involving FBIJobs.gov and claims made by ShinyHunters. The episode separates confirmed facts from unverified allegations, including a possible Oracle PeopleSoft zero-day, broader FBI system access, and claims that terabytes of data were stolen. Potentially affected entities include current and former FBI employees, agents, and FBI job applicants, whose sensitive PII could create risks beyond traditional identity theft. Atlas & Zero explore Zero Trust, network segmentation, MFA, privileged access, DLP, immutable logging, egress monitoring, service-account security, and vulnerability management while explaining how organizations can contain similar attacks.
In this week’s Cipher & Echo Cyber Brief, we examine a surge in active exploitation, ransomware, supply-chain attacks, and critical vulnerabilities. Cisco Secure Email Gateway and VMware vCenter face active threats, while Gyazo reports millions of exposed user records. Brevo confronts a widespread supply-chain attack, and Microsoft patches vulnerabilities across its cloud and AI platforms. We also investigate North Korea’s WaterPlum campaign, Iran-linked HEAVYGRAM and CHOSEN BRICK activity, and exploited vulnerabilities affecting Orkes Conductor, ConnectWise ScreenConnect, and Linux. Critical patches from Check Point, Kaspersky, and Tanium reinforce the week’s message: patch exploited systems, protect identities, segment infrastructure, and verify dependencies.
In this special episode of Atlas & Zero, we analyze the 2017 Equifax breach, one of the largest data compromises in history. Discover how attackers exploited the Apache Struts CVE-2017-5638 vulnerability after a security patch was already available. We examine the failures in vulnerability management, asset tracking, monitoring, segmentation, and security operations that allowed attackers to access sensitive consumer data.
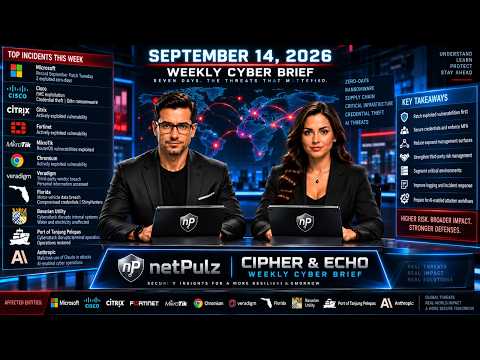
Microsoft faces exploited Windows zero-days, while vulnerabilities affecting Cisco, Citrix, Fortinet, MikroTik, and Chromium reinforce the urgency of patching exposed systems. Veradigm highlights third-party credential risk, while Florida motor-vehicle systems demonstrate the consequences of compromised access. Cyberattacks affecting a Bavarian utility and Malaysia’s Port of Tanjung Pelepas and more.
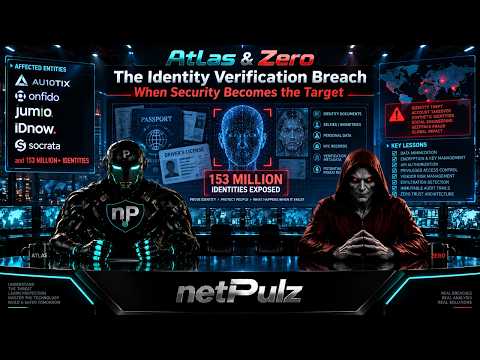
Atlas & Zero investigate the 153 Million IDs breach, examining how an attack against identity-verification infrastructure can transform security data into a powerful resource for criminals. The episode covers affected entities Connex Credit Union, Community Choice Credit Union, American First Credit Union, BrightStar Credit Union, ELGA Credit Union, and Alltrust Credit Union while exploring KYC architecture, encryption, and more.
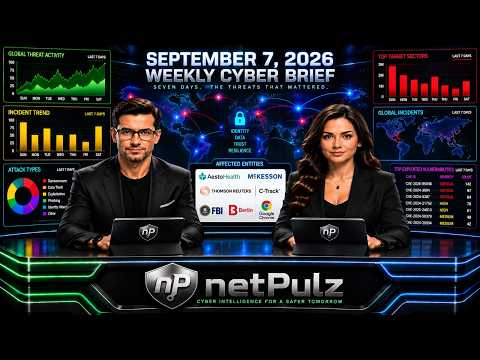
This week’s Cyber Brief examines how identity data, healthcare records, court systems, government networks, and browsers became high-value cyber targets. Cipher and Echo investigate the Aesto Health breach affecting millions, McKesson’s disclosed cyber incident, and unauthorized access involving Thomson Reuters C-Track court systems. The episode also covers CISA’s Known Exploited Vulnerabilities updates and more.
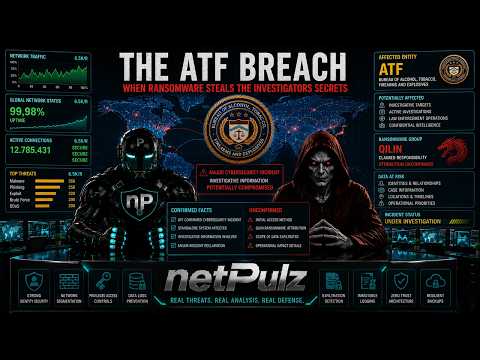
Atlas and Zero investigate the ATF cybersecurity breach, where sensitive information involving targets of Bureau of Alcohol, Tobacco, Firearms and Explosives investigations was potentially compromised. The Qilin ransomware group claimed responsibility, but its attribution and the initial access method remain unconfirmed. This episode separates verified facts from attacker claims while examining modern ransomware operations, and more.
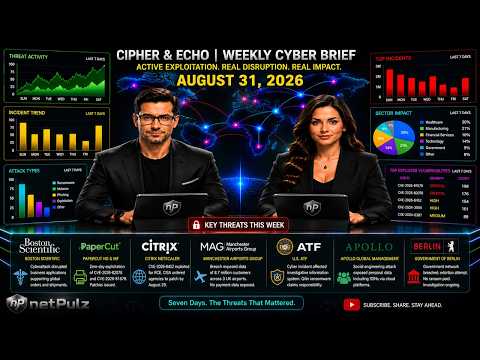
Cipher and Echo examine the cyberattack affecting Boston Scientific, actively exploited PaperCut NG/MF vulnerabilities, critical Citrix NetScaler exposure, and the Manchester Airports Group breach impacting millions of customers. The episode also covers the cyber incident involving the U.S. Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF), social-engineering-driven exposure at Apollo Global Management, and the cyberattack targeting the Government of Berlin.
In this Atlas & Zero Breach Analysis, we examine the NYC Health & Hospitals cyberattack that potentially exposed sensitive information belonging to 1.8 million people. The compromised data included medical information, Social Security numbers, financial information, credentials, fingerprints, and palm prints. Atlas and Zero explore how a third-party vendor breach may have enabled access, why trusted connections create serious security risks.
This week, attackers target the keys to critical systems: identities, cloud platforms, privileged access, and infrastructure. Cipher and Echo examine the Apollo Global and CareCloud breaches, Alation cyberattack, Medusa ransomware activity, exploited Windows vulnerabilities, and threats against industrial control systems.
In this episode of Atlas & Zero, we examine the Hugging Face attack and what it reveals about the emerging era of autonomous cyber threats. As artificial intelligence platforms process models, datasets, code, and automated workflows, traditional security boundaries are being challenged. Atlas and Zero explore malicious content, code execution, credential exposure, privilege escalation, lateral movement, and more.
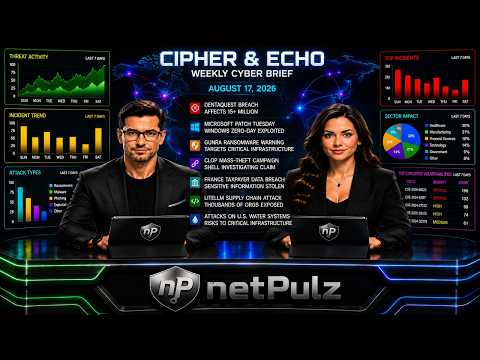
Cipher and Echo break down the cybersecurity threats shaping the week, from massive data breaches to actively exploited vulnerabilities. This episode examines the DentaQuest breach affecting millions, Microsoft Windows zero-day exploitation, Gunra ransomware targeting critical infrastructure, and Cl0p data-theft activity. The brief also covers the France taxpayer data breach and growing threats against U.S. water systems.
Join Cipher and Echo for the Weekly Cyber Brief covering August 2 through August 8, 2026. This episode examines the cybersecurity incidents, emerging threats, exploited vulnerabilities, and attacker activity that shaped the week. Cipher breaks down verified technical details, affected systems, vulnerabilities, and potential business impact, while Echo connects individual events to broader cyberattack trends.
This episode examines one of the most significant cybersecurity incidents in history, the SolarWinds supply chain attack. Discover how attackers infiltrated a trusted software build process, distributed malicious updates to thousands of organizations, and remained undetected for months. Atlas and Zero break down the complete attack timeline, technical methods, critical security failures, and the lessons every organization should learn.
Meet Atlas & Zero introduces the foundation of the netPulz cybersecurity universe. Atlas, the Cyber Guardian, and Zero, the Cyth Lord, represent two opposing perspectives on digital conflict: defense and adversarial thinking. Together, they explore real-world cyber attacks, revealing how breaches occur, why defenses fail, and what organizations can learn from them.
Get Started
Ready To Talk About Your Infrastructure?
Tell us what you are trying to build, modernize, secure, or support. We will review your request and follow up with the right next step.
See how netPulz can fit your environment.
Get help with infrastructure, AI, security, and operations.